GDPR & TCPA Compliance Guide for Enterprise WhatsApp Marketing
Enterprise messaging compliance requires explicit un-checked opt-in collection, automated unsubscribe keyword processing (e.g., STOP), and transparent data retention policies.
Table of Contents
Introduction: Navigating Messaging Regulations in 2026
Enterprise WhatsApp marketing requires strict compliance with global privacy regulations including GDPR (European Union), TCPA (United States), and local messaging consent laws. Fines for unsolicited commercial broadcast campaigns can be severe.
This legal guide outlines the mandatory steps your growth team must take to ensure 100% compliance across all broadcast campaigns.
1. What Constitutes a Valid WhatsApp Opt-In?
Under GDPR and TCPA, sending commercial WhatsApp messages requires explicit, informed consent obtained prior to dispatch:
- Website Capture Forms: Consent checkboxes must be unchecked by default. The checkbox text must explicitly mention WhatsApp communications.
- Inbound Chat Initiations: When a customer initiates a chat first for support, implied consent covers the 24-hour service window. Marketing follow-ups require explicit opt-in.
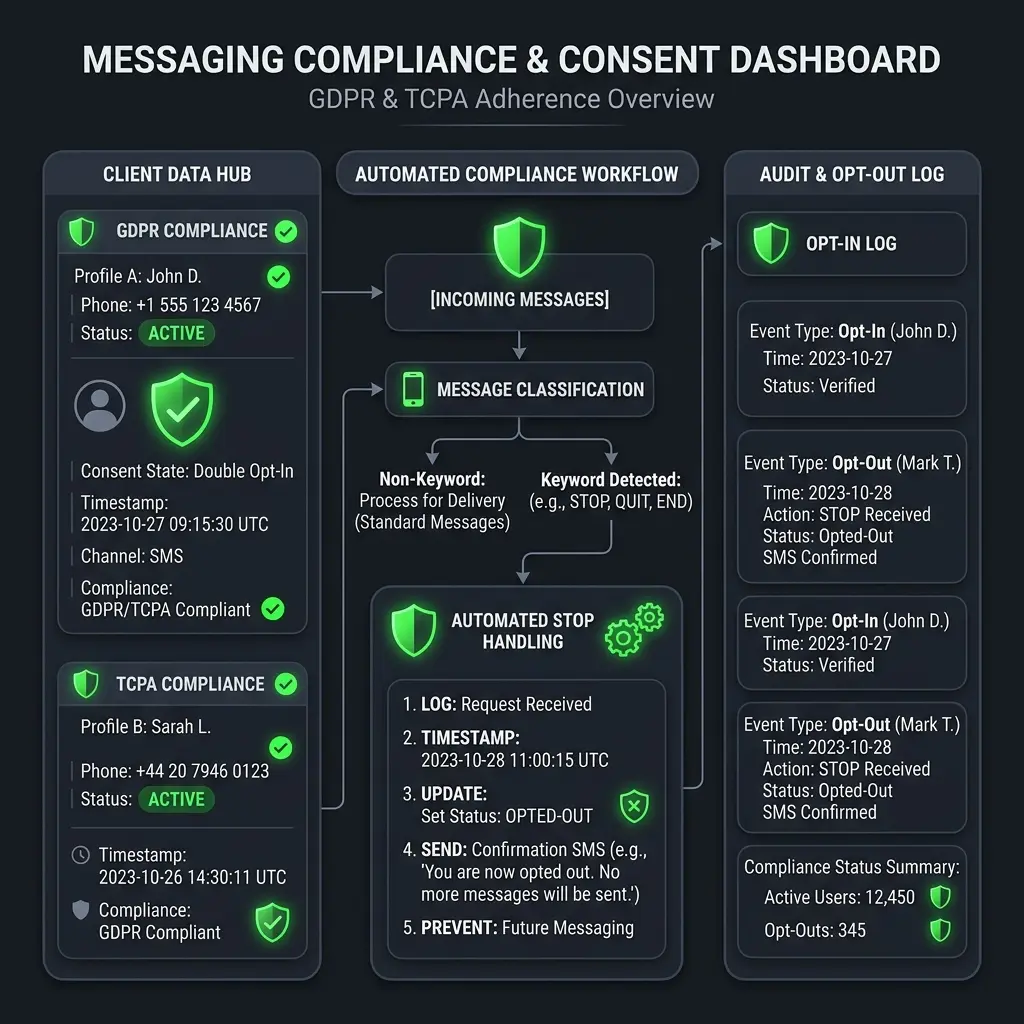
- Consent Audit Trail: Patify logs the date, IP address, and opt-in source timestamp for every subscriber record.
2. Automated Opt-Out & Contact Purge Protocols
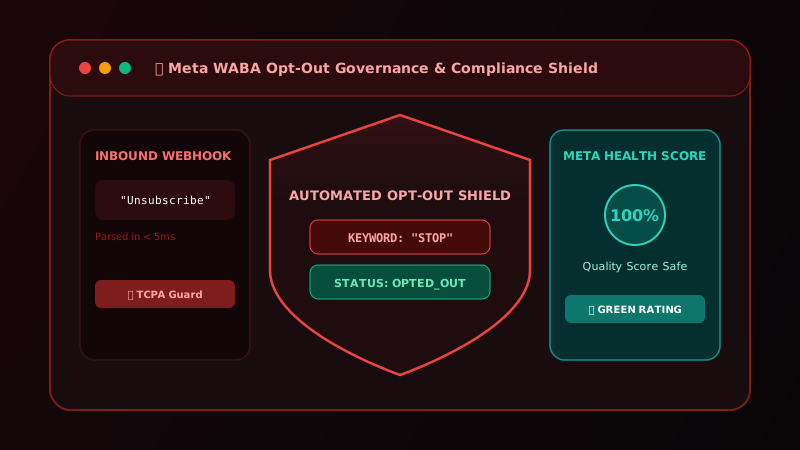
When a recipient replies with "STOP", "UNSUBSCRIBE", or taps a decline button, Patify automatically updates their contact status to unsubscribed and halts future broadcasts instantly. Use custom contact tags to enforce opt-out segments across all campaigns.
3. Data Retention & Right-to-Be-Forgotten Compliance
In accordance with GDPR Article 17, subscribers can request full data erasure. Patify's BYOK data architecture ensures your business retains full ownership of customer data — Patify provides bulk contact purging tools to delete phone numbers and message logs permanently.
Ensure Your Messaging Compliance
Set up automated double opt-in audit logs and STOP unsubscribe processing